Cybersecurity advisory and compliance, from requirements to implementation.
Syperium helps organizations assess cybersecurity risks, identify control gaps, strengthen security programs, and navigate compliance requirements.With specialized experience in CMMC and NIST SP 800-171, Syperium helps defense contractors, subcontractors, and small businesses navigate cybersecurity requirements through practical GRC advisory, remediation, and implementation support.
Cybersecurity & Compliance Services
Syperium helps organizations assess cybersecurity risks, strengthen control environments, improve documentation, and prepare for compliance assessments.
Assess
Cybersecurity & Compliance Assessments
Understand your current security posture, identify control gaps, and determine where remediation should be prioritized.
| What You Get | |
|---|---|
| • Gap analysis | • Identified control deficiencies |
| • Prioritized findings | • Recommended next steps |
Advise
Remediation Planning & GRC Advisory
Turn assessment findings into a practical and risk-informed plan for addressing cybersecurity and compliance requirements.
| What You Get | |
|---|---|
| • Remediation roadmap | • Corrective action guidance |
| • Implementation priorities | • Risk-based recommendations |
Implement
Control Implementation & Documentation Support
Syperium works alongside internal IT teams and managed service providers (MSPs) to guide security control implementation, develop compliance documentation, and coordinate remediation efforts.For organizations without dedicated IT resources, Syperium can provide or coordinate technical implementation support based on organizational needs.
| What You Get | |
|---|---|
| • Security policies & procedures | • System Security Plan (SSP) support |
| • Control implementation guidance | • POA&Ms development |
Validate
Assessment Readiness & Ongoing Support
Prepare for assessments by reviewing evidence, validating progress, and helping maintain ongoing compliance readiness.
| What You Get | |
|---|---|
| • Evidence Readiness Review | • Assessment preparation support |
| • Corrective Action tracking | • Ongoing advisory support |
Specialized Framework Support
CMMC & NIST SP 800-171
Focused support for organizations in the Defense Industrial Base seeking to assess, implement, document, and maintain cybersecurity requirements.
Cybersecurity Risk & Governance Frameworks
Risk assessments, control evaluations, and security program improvement support informed by established cybersecurity frameworks and industry practices.
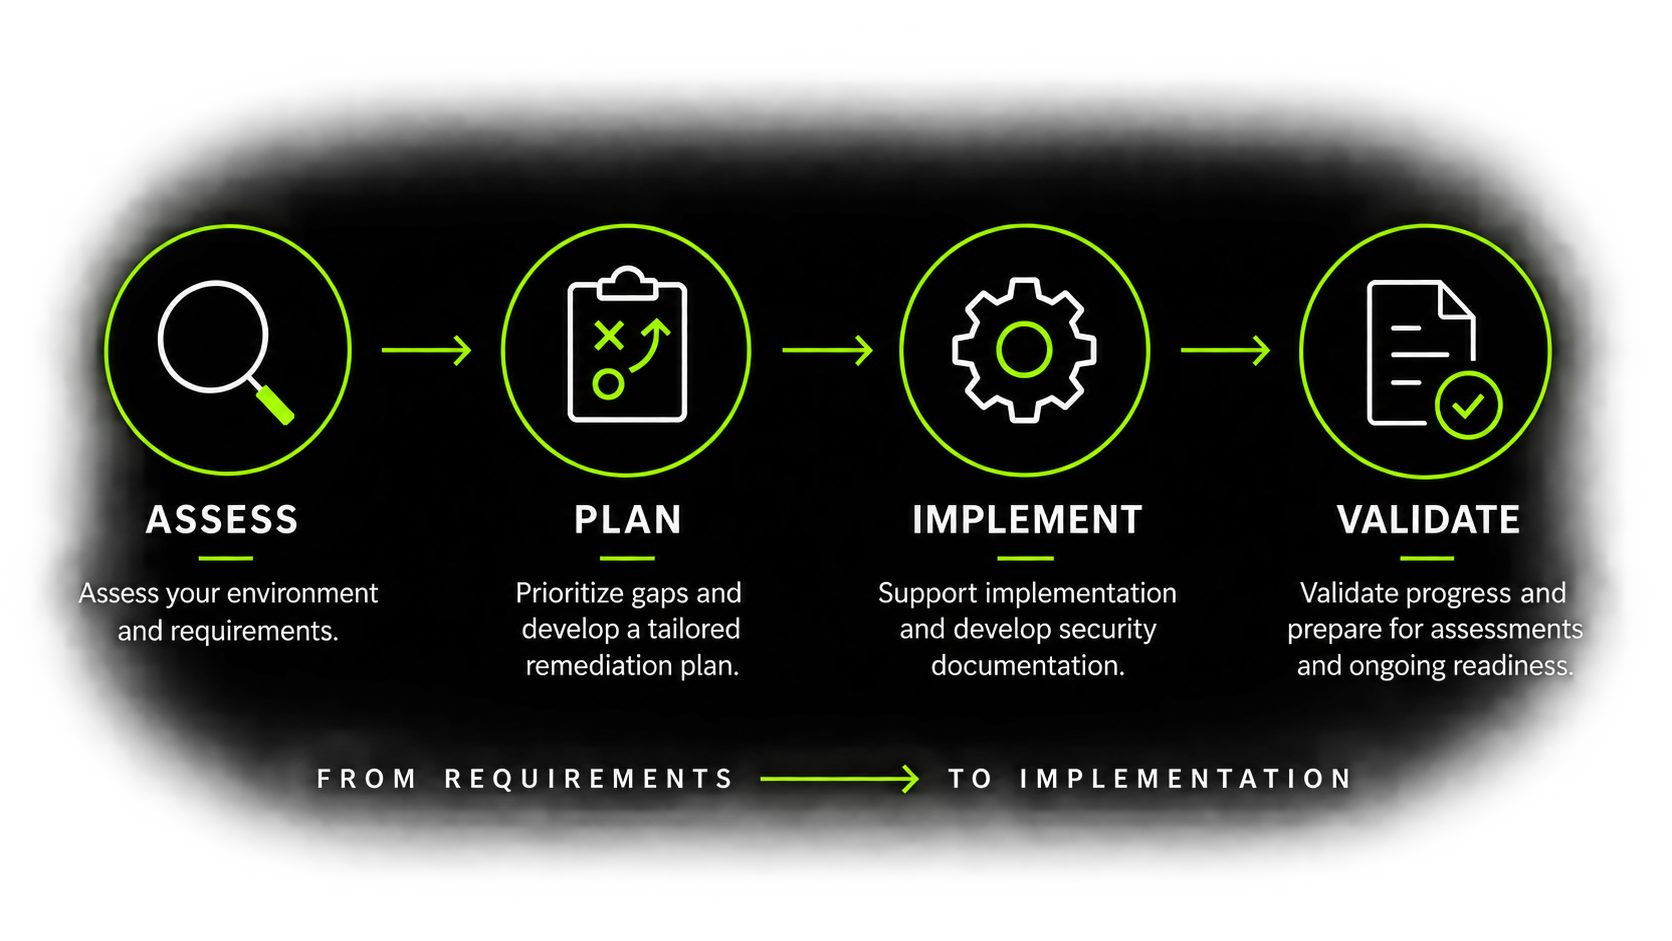
Methodology
From Requirements to Implementation
Syperium uses a structured approach to move cybersecurity requirements from interpretation through implementation and readiness.
Discuss Your Cybersecurity Needs
Whether you need a cybersecurity assessment, remediation support, or ongoing GRC guidance, Syperium can help you identify the right next steps.
About Syperium
Built to Make Cybersecurity Requirements Actionable
Cybersecurity requirements often define what organizations must achieve without clearly explaining how to get there. For small and mid-sized organizations, translating those requirements into effective controls can be challenging without dedicated cybersecurity and compliance resources.Syperium was established to help bridge that gap.We provide practical cybersecurity GRC advisory and implementation support to help organizations identify risks, address compliance requirements, strengthen security controls, and maintain assessment readiness.
The Experience Behind Syperium
Chris J. Gonzalez
Founder / Principal ConsultantCertified CMMC Assessor (CCA)
Certified CMMC Professional (CCP)
ISC2 Certified in Governance, Risk and Compliance (CGRC)
Chris brings five years of cybersecurity and compliance experience, with a focus on NIST SP 800-171, CMMC, and organizations within the Defense Industrial Base.His background includes assessing and documenting security controls, supporting remediation and implementation, preparing assessment evidence, and conducting recurring IT audit and compliance activities.His experience also includes working in a C3PAO environment and participating on a team that underwent a DIBCAC assessment during the organization's C3PAO authorization process. This provided direct exposure to the documentation, evidence, and control implementation expectations associated with formal assessments.
A Practical Approach
Syperium begins by understanding each organization's environment, applicable requirements, and current cybersecurity posture.From there, we identify meaningful control gaps, prioritize remediation efforts, and support practical improvements aligned with the organization's resources and operational needs.Our focus extends beyond documenting compliance. We help organizations develop security controls and processes that can be implemented, maintained, and supported by reliable evidence.
Discuss Your Cybersecurity Needs
Whether you need assessment support, remediation guidance, or ongoing GRC advisory, Syperium can help identify a practical path forward.
Contact Syperium
Have a cybersecurity requirement, compliance question, or security challenge you need help working through?Contact Syperium to discuss your environment, what you are trying to accomplish, and the appropriate next steps.